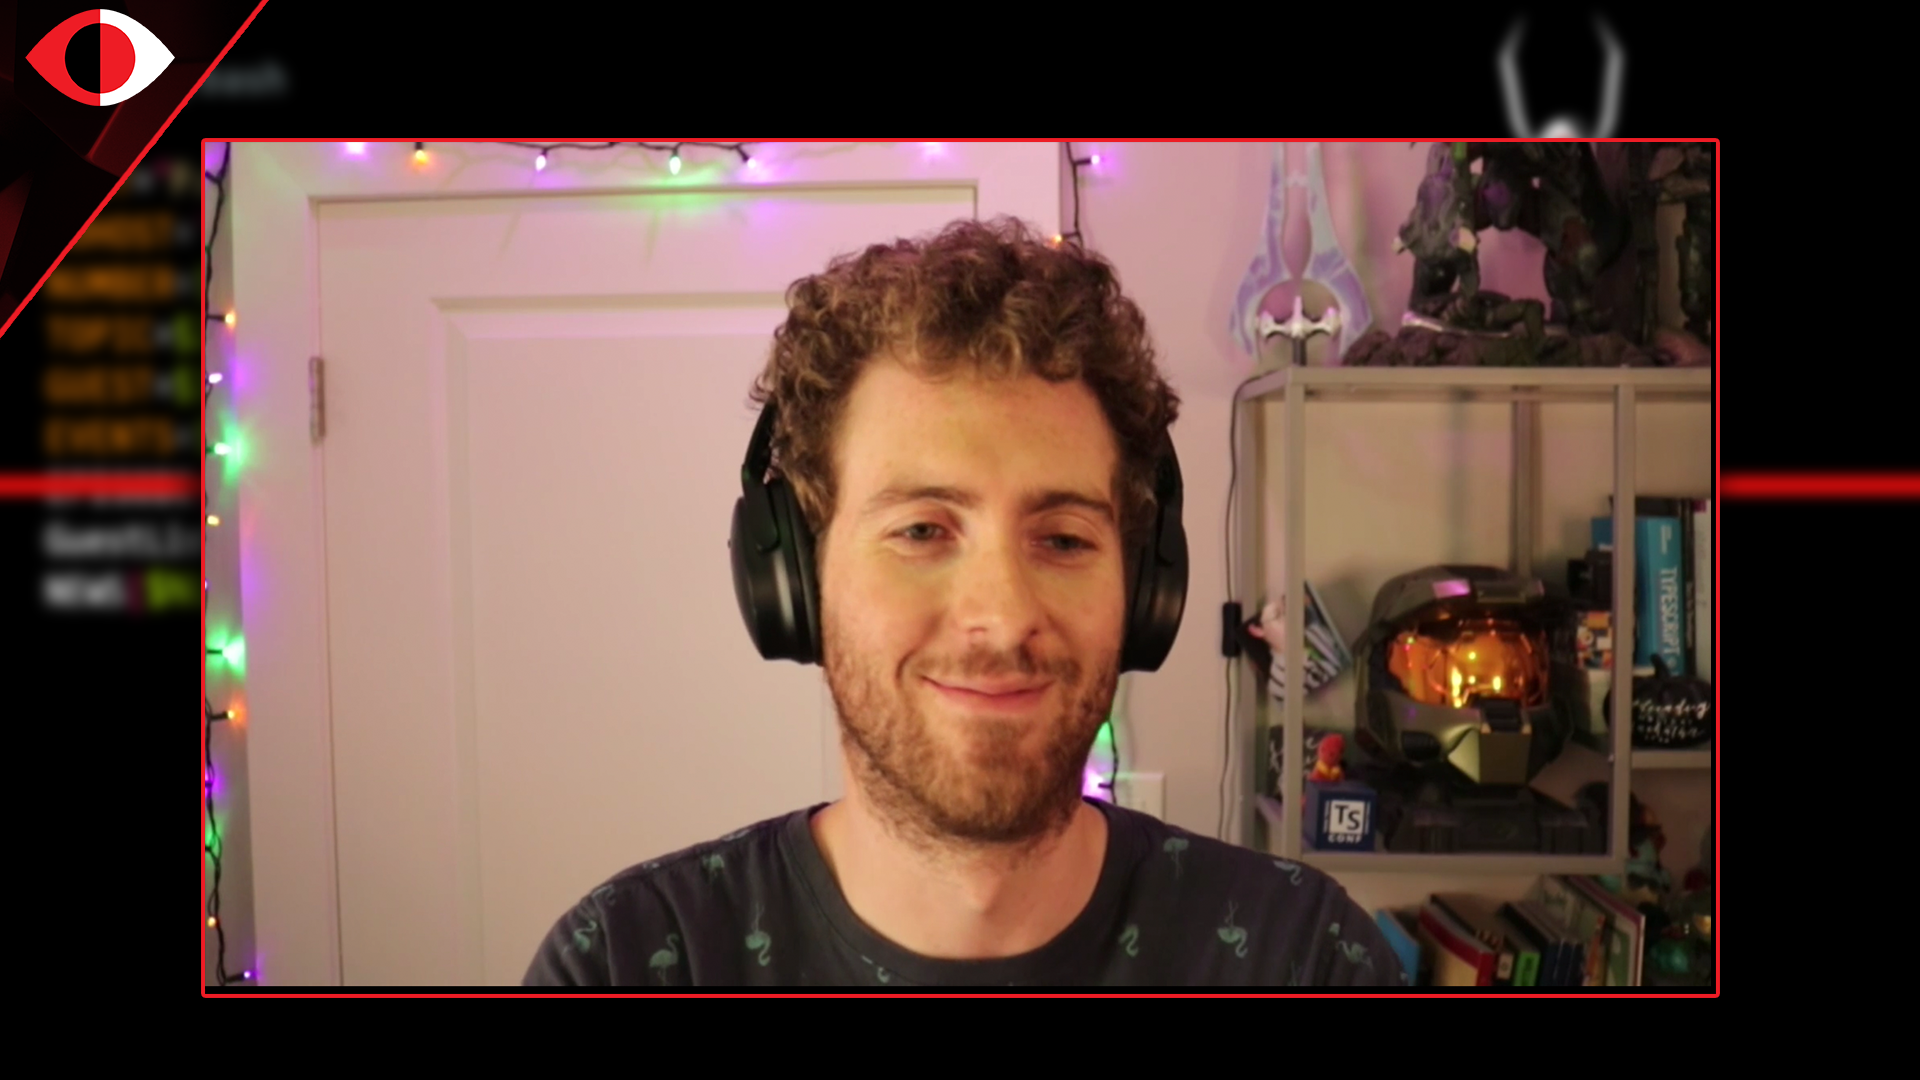
ASW #233 - Josh Goldberg
Static analysis is the art of scrutinizing your code without building or running it. Common static analysis tools are formatters (which change whitespace and other trivia), linters (which detect likely best practice and style issues), and type checkers (which detect likely bugs). Each of these can aid in improving application security by detecting real issues at development-time. Segment Resources: https://typescript-eslint.io https://eslint.org https://blog.joshuakgoldberg.com Outlook can leak NTLM hashes, potential RCE in a chipset for Wi-Fi calling in phones (and autos!?), the design of OpenSSH's sandboxes, more on the direction of OWASP, celebrating 25 years of Curl. Visit https://www.securityweekly.com/asw for all the latest episodes! Follow us on Twitter: https://www.twitter.com/secweekly Like us on Facebook: https://www.facebook.com/secweekly Show Notes: https://securityweekly.com/asw233
You May Also Like
AI News Daily
brief.news

Artificial Intelligence Masterclass
AI Masterclass

Tech Brew Ride Home
Morning Brew

The Vergecast
The Verge
The Rollup
Where digital assets and finance converge. Hosted by Andy and Robbie.
Radio Miraya
Radio Miraya

Mark Tilbury
Mark Tilbury Fan

Jack Hopkins
Jack Hopkins
AI Unraveled: Latest AI News & Trends, ChatGPT, Gemini, DeepSeek, Gen AI, LLMs, Agents, Ethics, Bias
Etienne Noumen
The Geoholics
thegeoholics
AI News Daily
brief.news
Artificial Intelligence Masterclass
AI Masterclass
Tech Brew Ride Home
Morning Brew
The Vergecast
The Verge
The Rollup
Where digital assets and finance converge. Hosted by Andy and Robbie.
Radio Miraya
Radio Miraya
Mark Tilbury
Mark Tilbury Fan
Jack Hopkins
Jack Hopkins
AI Unraveled: Latest AI News & Trends, ChatGPT, Gemini, DeepSeek, Gen AI, LLMs, Agents, Ethics, Bias
Etienne Noumen
The Geoholics
thegeoholics
Community discussion