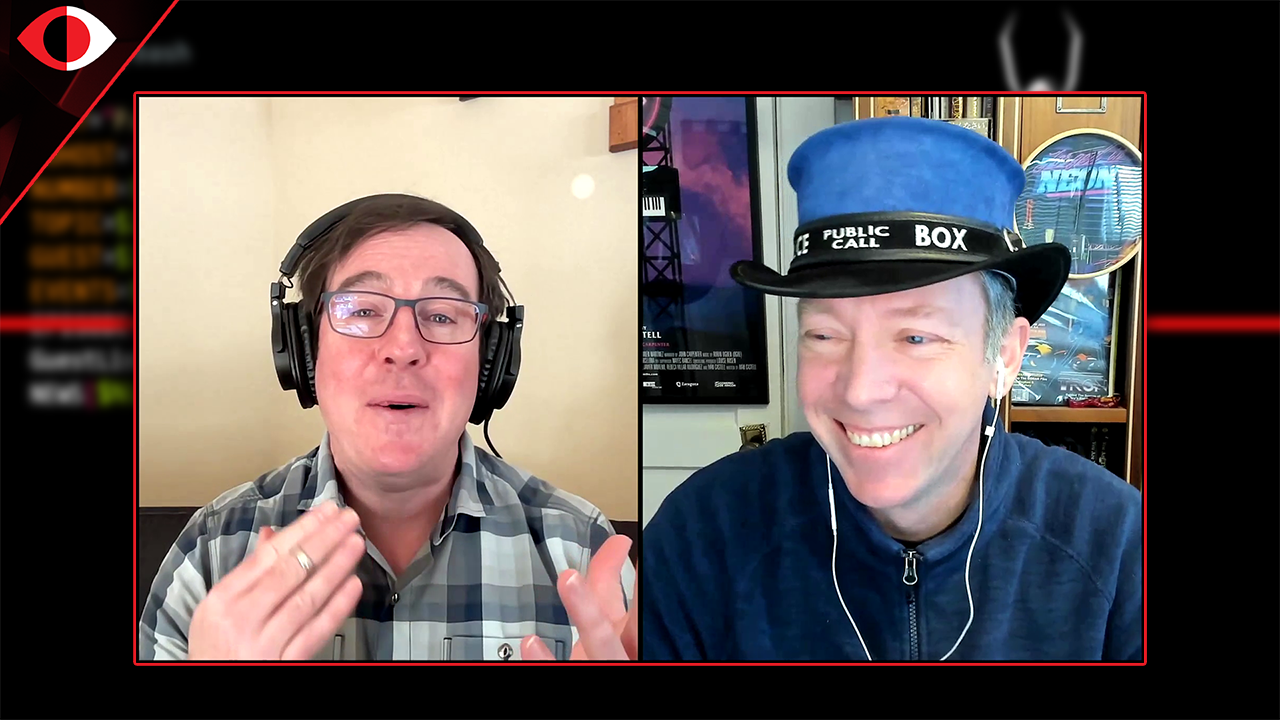
Throwback Episode - ASW #178
It's another holiday week, so enjoy this episode from our archives! What does a collaborative approach to security testing look like? What does it take to tackle an entire attack class as opposed to fixing a bunch of bugs? If we can shift from vulnerability mitigation to vulnerability elimination, then appsec would be able to demonstrate some significant wins -- and they need a partnership with DevOps teams in order to do this successfully. Log4j has more updates and more vulns (but probably not more heartburn...), revisiting outages and whether availability has made it into your threat models, deep dive into hardware security, another data point on bug bounty awards, and looking at risk topics for the next year. This completes another year of the podcast! A very heartfelt thank you to all our listeners! And a special thank you and shout out to the crew that helps make this possible every week -- Johnny, Gus, Sam, and Renee. We'll keep the New Wave / Post-Punk, movie, and pop culture references coming for all the appsec and DevOps topics you can throw our way. Thanks again everyone!! Segment Resources: - https://blog.trailofbits.com/ Show Notes: https://securityweekly.com/asw178
You May Also Like

Theo - t3․gg
Theo - t3․gg

Jak Piggott
Jak Piggott

The AI Daily Brief: Artificial Intelligence News and Analysis
Nathaniel Whittemore

Proof of Law
Quantum Lex
AI News Daily
brief.news

Artificial Intelligence Masterclass
AI Masterclass

Tech Brew Ride Home
Morning Brew

The Vergecast
The Verge
The Rollup
Where digital assets and finance converge. Hosted by Andy and Robbie.

Late Night Linux Family All Episodes
The Late Night Linux Family
Theo - t3․gg
Theo - t3․gg
Jak Piggott
Jak Piggott
The AI Daily Brief: Artificial Intelligence News and Analysis
Nathaniel Whittemore
Proof of Law
Quantum Lex
AI News Daily
brief.news
Artificial Intelligence Masterclass
AI Masterclass
Tech Brew Ride Home
Morning Brew
The Vergecast
The Verge
The Rollup
Where digital assets and finance converge. Hosted by Andy and Robbie.
Late Night Linux Family All Episodes
The Late Night Linux Family
Community discussion