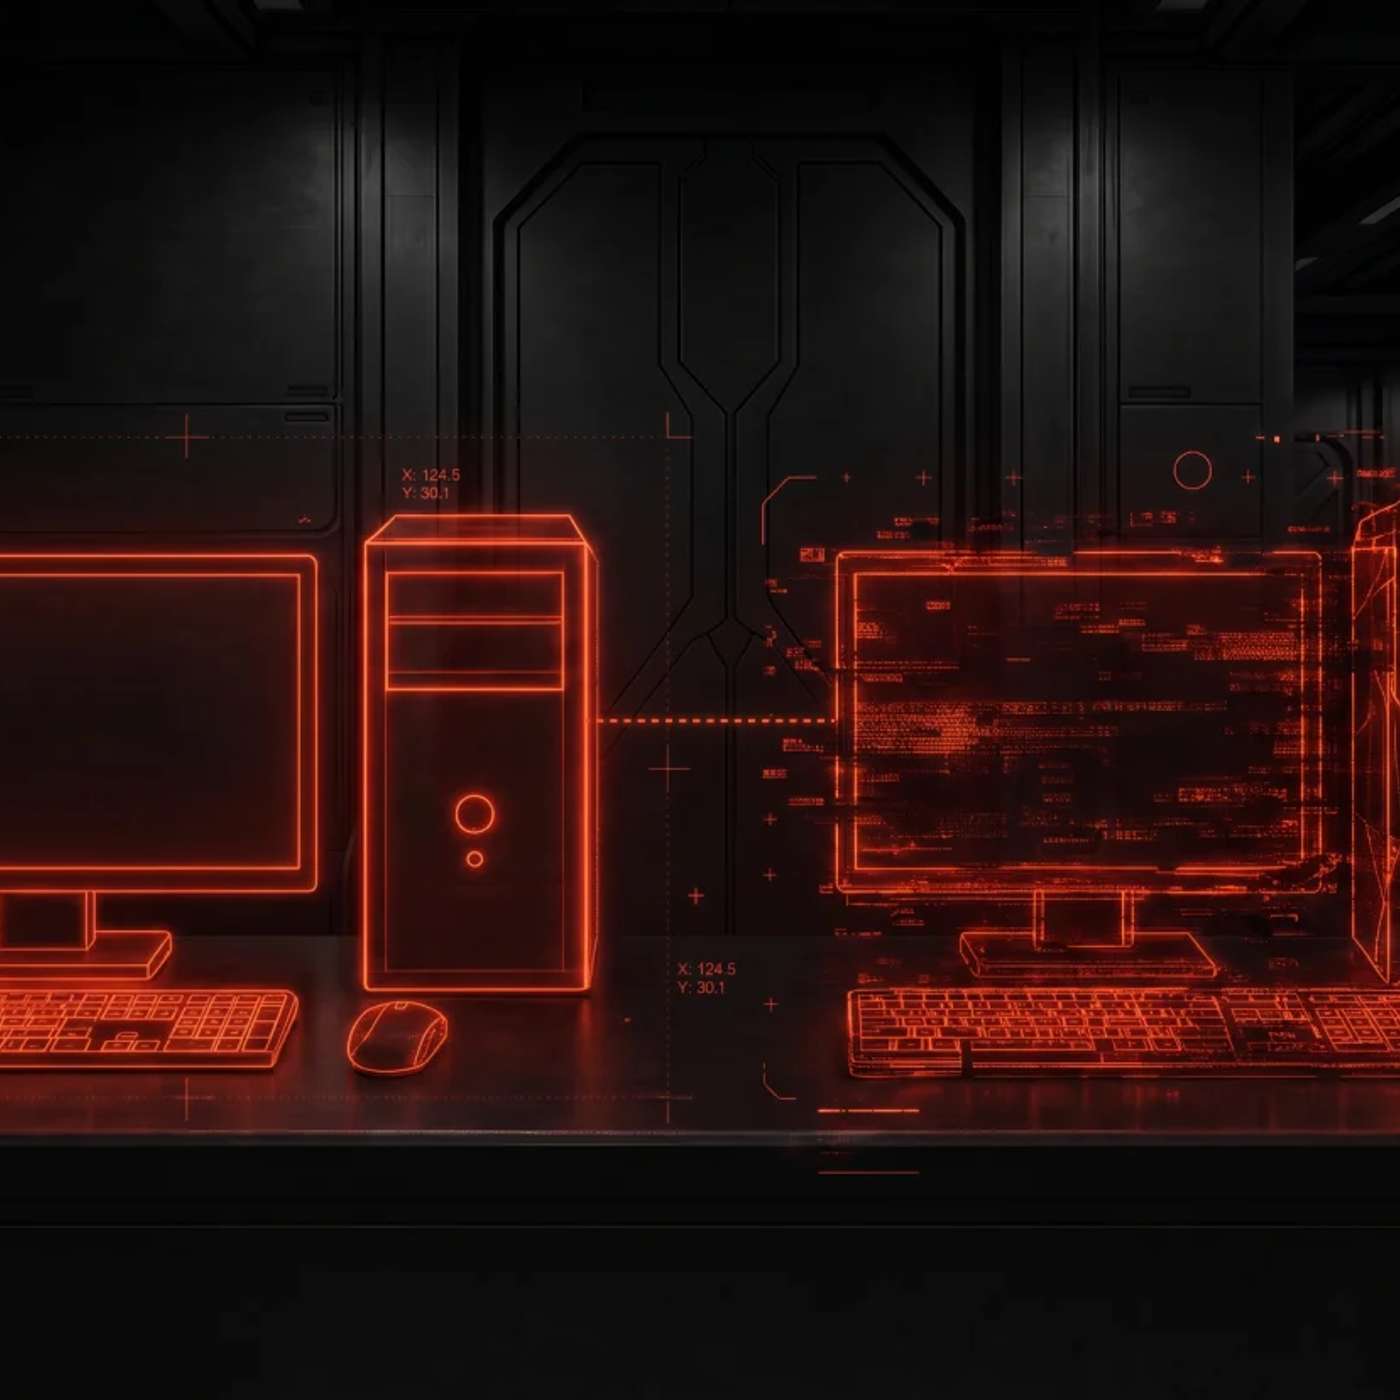
Meet AvisLoader: A Windows Loader Built to Outlast a Takedown
This story was originally published on HackerNoon at: https://hackernoon.com/meet-avisloader-a-windows-loader-built-to-outlast-a-takedown.
Discover how AvisLoader uses Tox peer-to-peer messaging for C2, ClickFix delivery, shortcut persistence, and payload distribution without fixed domains.
Check more stories related to undefined at: https://hackernoon.com/c/undefined. You can also check exclusive content about #avisloader-malware, #tox-peer-to-peer-malware, #windows-malware-loader, #clickfix-malware-campaign, #tox-based-c2-communication, #avisloader-varonis-threat-labs, #avisloader-tox-c2, #good-company, and more.
This story was written by: @varonis. Learn more about this writer by checking @varonis's about page, and for more stories, please visit hackernoon.com.
Varonis Threat Labs discovered AvisLoader, a Windows malware loader that uses the encrypted Tox peer-to-peer network for command-and-control communication and payload delivery. Found alongside a ClickFix lure and operator Command Center, the loader combines shortcut persistence, a bundled UAC bypass helper, and process-hiding functionality. Its Tox-based architecture makes domain-focused takedowns harder, while host activity provides additional detection opportunities for security teams.
You May Also Like

Jack Hopkins
Jack Hopkins
Search Engine
PJ Vogt

Jak Piggott
Jak Piggott
硅谷101
硅谷101

AI Fire Daily
AIFire.co

The Daily AI Show
The Daily AI Show Crew - Brian, Beth, Jyunmi, Andy and Karl
Tech&Co, la quotidienne
BFM Business

The AI Daily Brief: Artificial Intelligence News and Analysis
Nathaniel Whittemore
TBPN
John Coogan & Jordi Hays

The Vergecast
The Verge
Jack Hopkins
Jack Hopkins
Search Engine
PJ Vogt
Jak Piggott
Jak Piggott
硅谷101
硅谷101
AI Fire Daily
AIFire.co
The Daily AI Show
The Daily AI Show Crew - Brian, Beth, Jyunmi, Andy and Karl
Tech&Co, la quotidienne
BFM Business
The AI Daily Brief: Artificial Intelligence News and Analysis
Nathaniel Whittemore
TBPN
John Coogan & Jordi Hays
The Vergecast
The Verge
Community discussion